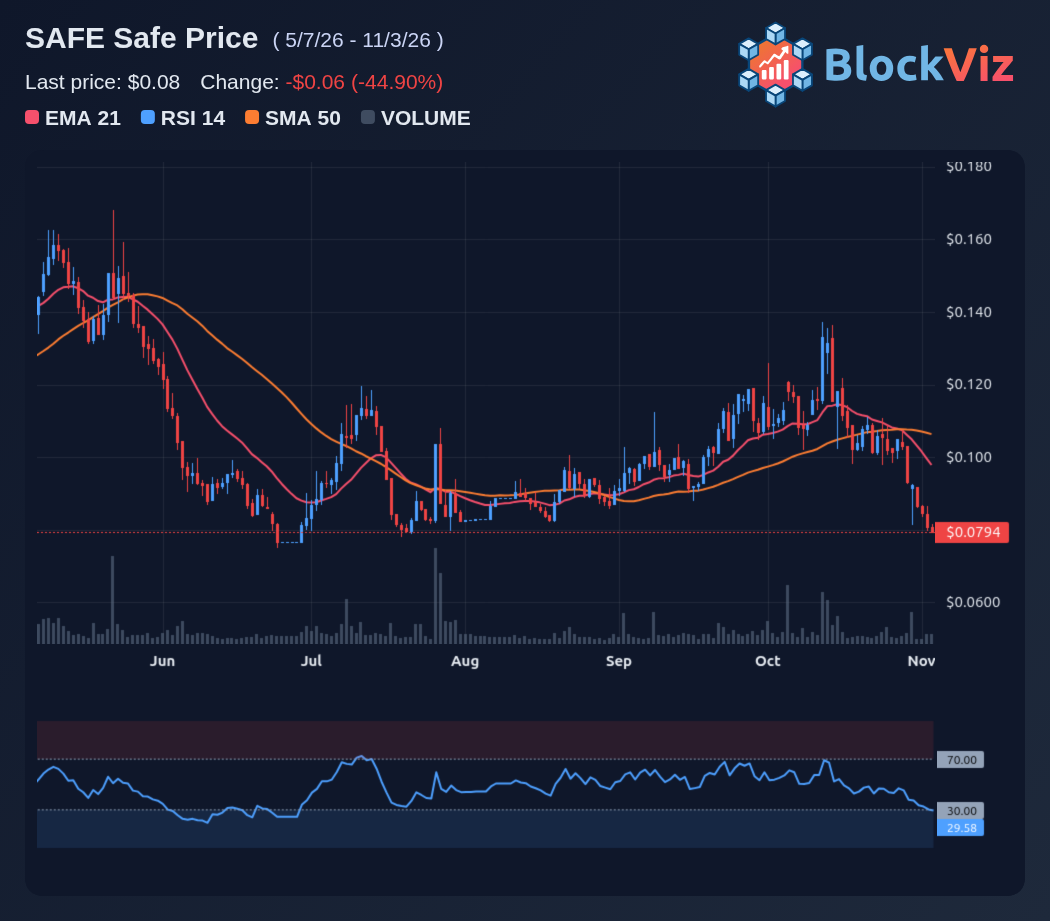
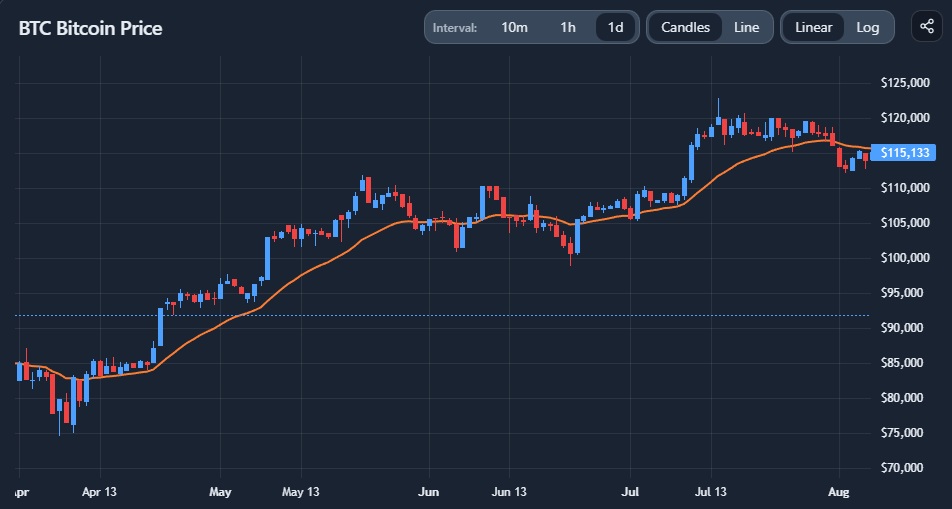
Three more hacks after Binance raise a harder question: is the weak point one exchange, or the custodial model itself?
If attackers are targeting withdrawal systems, API keys, vendors, or insiders, solvency is only part of the risk. Hot wallets, customer data, and withdrawal controls all expand the attack surface.
Self-custody removes exchange counterparty risk, but it does not remove security risk. Phishing, malicious approvals, compromised devices, and fake recovery prompts can still drain funds.
The key signals now are whether the incidents share one attack vector, whether withdrawals slow or pause, and how stolen funds move. Platforms will be judged by what failed, what was contained, and whether customer assets remained protected.